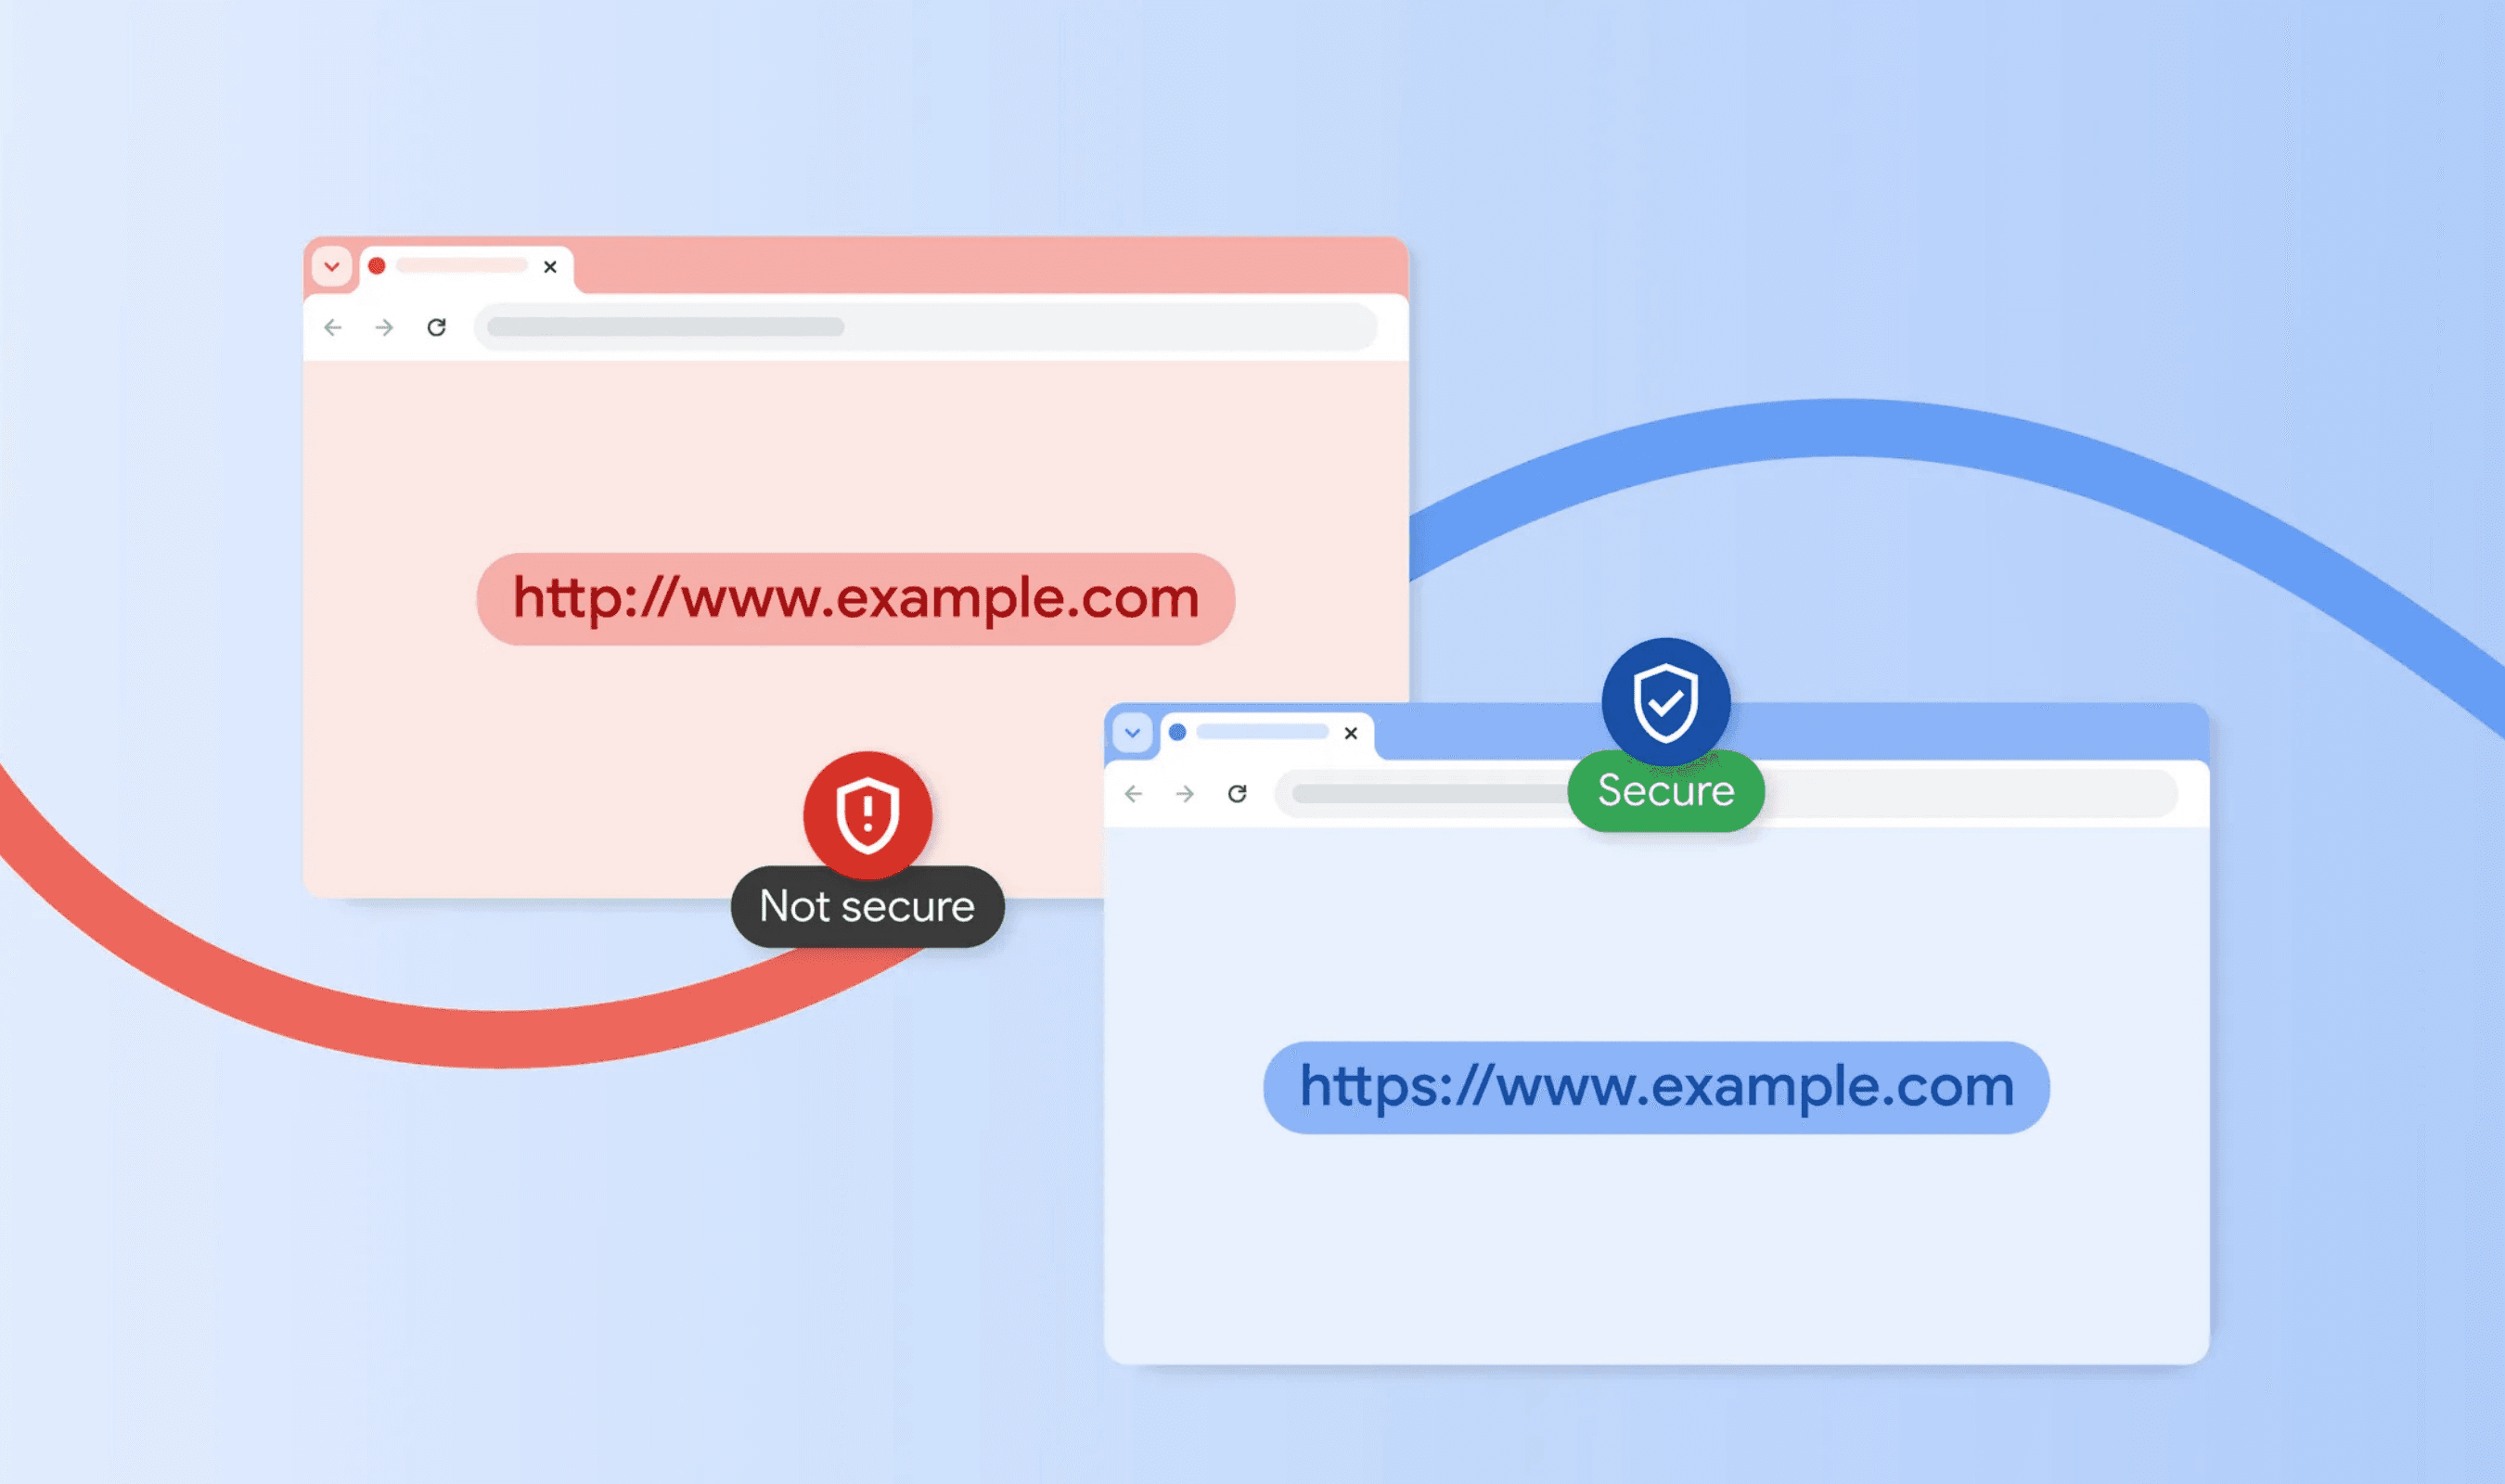
Google has blocked compromised eMudhra certificate keys in Chrome, with equivalent protection delivered to Android devices and Googlebooks through Google Play Services. Most Android devices have received the fix, and users can restart their device to trigger it immediately. Chrome's protection required neither a browser upgrade nor a restart.
The Chrome Root Program received a researcher's report at 18:05 UTC on October 17 about compromised private keys for eight eMudhra subordinate Certification Authority certificates. Insufficient randomness during key generation made it possible for anyone to create trusted HTTPS certificates impersonating any website on clients still trusting those authorities.
Read more: Google Blocks 7 Billion Malicious Chrome Notifications Daily With Swiss Cheese Model
Chrome verified the findings and implemented a CRLSet block at 19:45 UTC that day, targeting Subject Public Key Info hashes to cover every certificate using the affected keys. Android devices and Googlebooks received their equivalent update around 22:00 UTC on Monday.
Google also removed emSign ECC Root CA - G3 from its root store, with distribution expected Tuesday morning, October 27, PDT, and earlier through Chrome Canary and Chrome Beta. That step will also cause some legitimate certificates to stop working in Chrome. Affected website operators must immediately replace their TLS certificates using another hierarchy trusted by the Chrome Root Store; eMudhra has committed to helping subscribers migrate.
Google says no TLS certificates linked to six intermediate CAs appeared in Certificate Transparency logs before the block, preventing fraudulent certificates from working against clients enforcing those checks. Those include Chrome by default and Android apps targeting the latest SDK or otherwise opting in.
Google found no other root-store keys with the same randomness problem and coordinated remediation with browser vendors, root-store operators and software maintainers. Certificate Transparency logs now reject certificates linked to the compromised authorities, and Google is investigating whether eMudhra's remaining CA certificates should retain trust.